Cross-Site Scripting (XSS) Explained: Attacks and Prevention
Imagine visiting a trusted website, logging into your account, and unknowingly executing malicious JavaScript planted by a cybercriminal. The website itself may be legitimate, but a vulnerability...
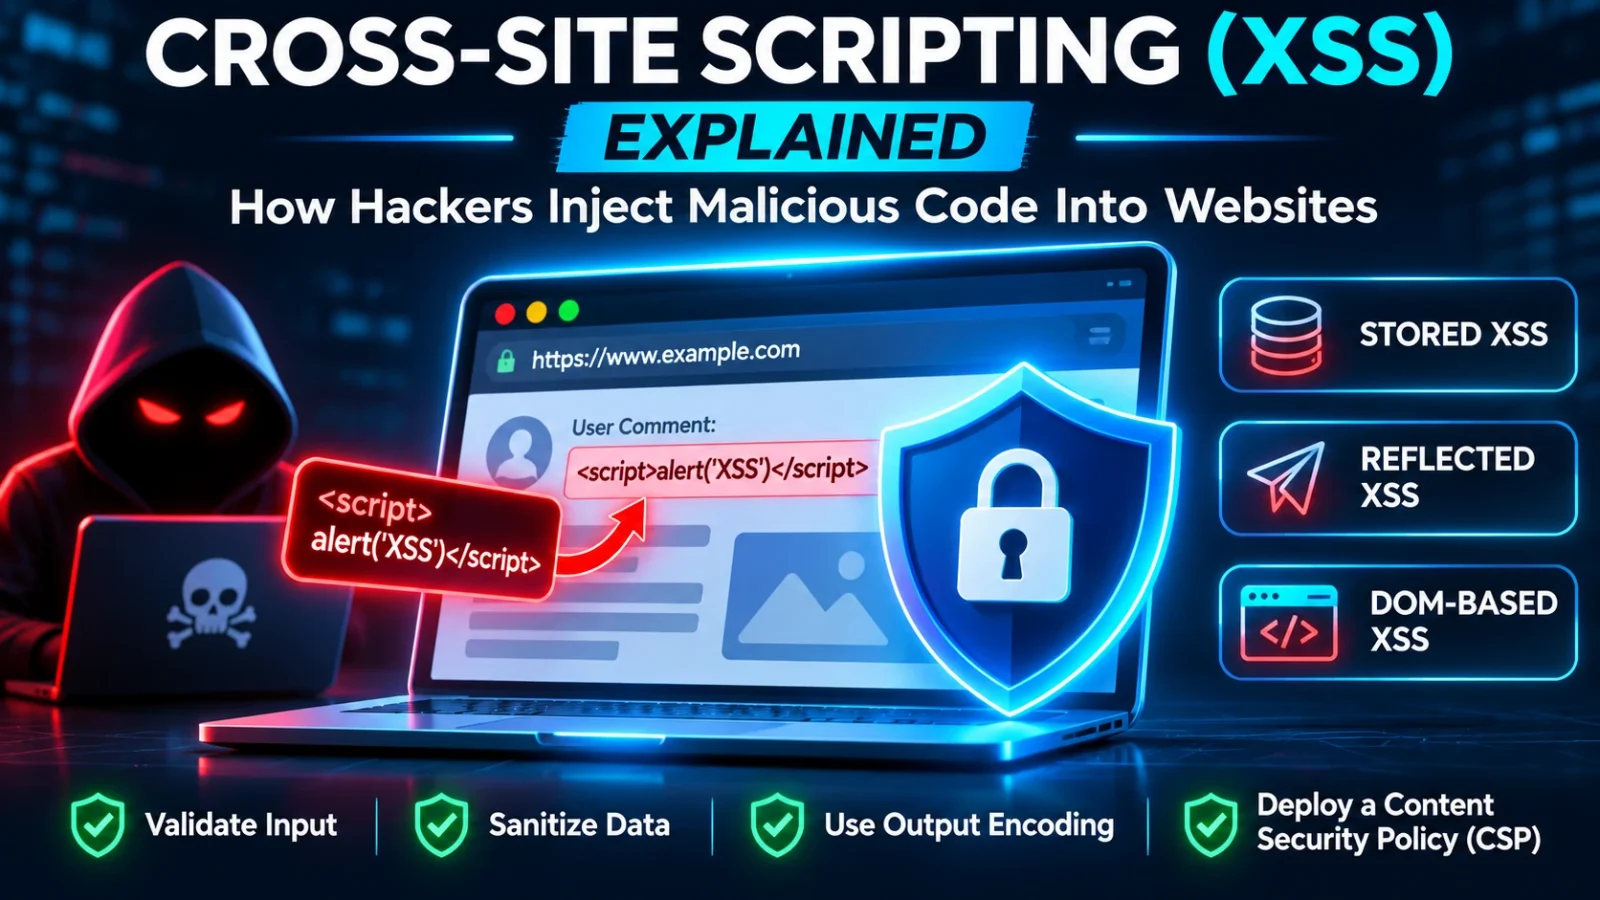
Imagine visiting a trusted website, logging into your account, and unknowingly executing malicious JavaScript planted by a cybercriminal.
The website itself may be legitimate, but a vulnerability allows an attacker to inject code that runs inside your browser.
This is known as Cross-Site Scripting (XSS), a common web application vulnerability that can expose sensitive information, manipulate website content, and compromise user accounts.
Understanding how XSS works is essential for developers, website administrators, and businesses operating online platforms.
1. What Is Cross-Site Scripting (XSS)?
Cross-Site Scripting occurs when a web application allows untrusted information to be interpreted as executable code inside a user's browser.
For example, a vulnerable website might display user-submitted comments without properly handling HTML and JavaScript.
An attacker could exploit this weakness to introduce malicious content that executes when another user views the page.
Because the code runs within the website's security context, it may interact with information and functionality available to the affected user.
Cybersecurity insight: XSS does not necessarily require hackers to compromise the web server. A vulnerable application can unintentionally deliver malicious code to its own visitors.
2. The Three Main Types of XSS Attacks
Stored XSS (Persistent XSS)
Stored XSS occurs when malicious content is saved by an application and later displayed to other users.
For example, an attacker might submit malicious content through a vulnerable comment section, customer review, or profile field.
If the application renders the content unsafely, visitors may execute the attacker's JavaScript when viewing the affected page.
Stored XSS is especially concerning because one malicious entry can potentially affect multiple users.
Reflected XSS (Non-Persistent XSS)
Reflected XSS occurs when a website immediately includes untrusted request data in its response without making it safe.
For example, a search page might display a user's search query directly in the resulting HTML.
An attacker could create a specially crafted link containing malicious input and attempt to convince someone to open it.
If the application is vulnerable, the browser may interpret the reflected content as executable code.
DOM-Based XSS
DOM-based XSS arises when JavaScript running in the browser handles untrusted data unsafely.
For example, a website might read information from the page URL and insert it into the document using an unsafe HTML-rendering API.
If the application interprets that information as HTML rather than plain text, malicious code may execute.
Unlike many server-rendered XSS vulnerabilities, this issue can occur entirely within client-side JavaScript.
Technical note: Stored and reflected describe how malicious content reaches the victim, while DOM-based describes unsafe processing in the browser. These classifications can overlap.
3. What Can Hackers Do With XSS?
The consequences depend on the application's permissions, security configuration, and the victim's account.
A successful XSS attack may allow cybercriminals to:
Hijack accounts: Perform unauthorized actions within an authenticated session.
Steal sensitive information: Access data available to scripts within the application's security context.
Manipulate website content: Display fraudulent messages or alter visible information.
Launch phishing attacks: Present deceptive login forms within an otherwise legitimate website.
Perform unauthorized transactions: Abuse application functionality accessible to the victim.
XSS does not automatically give an attacker access to the operating system or every account in the browser.
However, it can still cause serious damage when vulnerable applications handle sensitive business information.
4. A Realistic XSS Attack Scenario
Consider an online customer-support portal where employees manage support tickets.
An attacker submits a ticket containing malicious content.
The application stores the ticket in its database but fails to safely render the submitted information.
When an administrator opens the ticket, the malicious JavaScript executes in the administrator's browser.
Depending on the application's security controls, the attacker may be able to abuse the administrator's authenticated session or access information visible to that account.
This demonstrates why XSS vulnerabilities can be particularly dangerous in administrative dashboards and business management applications.
5. How Can Developers Prevent XSS?
Preventing Cross-Site Scripting requires secure coding practices and multiple layers of protection.
1. Use Context-Aware Output Encoding
Untrusted information must be safely encoded according to where it appears, such as HTML text, attributes, or JavaScript string contexts.
Modern frameworks often provide automatic escaping, but developers must avoid bypassing these protections.
2. Avoid Unsafe JavaScript Functions
Avoid inserting untrusted content directly through APIs such as innerHTML or document.write().
For plain text, use safer approaches:
element.textContent = userInput;
This displays the information as text rather than interpreting it as HTML.
3. Sanitize User-Provided HTML
If users must submit formatted HTML, use a maintained HTML sanitization library such as DOMPurify.
Input validation alone is not sufficient protection against XSS.
4. Implement Content Security Policy (CSP)
A properly configured CSP can restrict which scripts browsers are permitted to execute.
Nonce-based or hash-based policies provide valuable additional protection against certain injection attacks.
However, CSP should complement secure coding, not replace it.
5. Use Secure Session Cookies
Configure session cookies with appropriate HttpOnly, Secure, and SameSite attributes.
These controls reduce certain risks, including direct access to HttpOnly cookies from JavaScript, but they do not eliminate XSS.
6. Test Your Applications Regularly
Conduct secure code reviews, authorized penetration testing, and application security assessments.
For JavaScript-heavy applications, consider Trusted Types where supported to reduce unsafe DOM injection.
6. Why XSS Matters for Businesses
A single XSS vulnerability can affect customer portals, e-commerce websites, WordPress plugins, healthcare platforms, and internal business applications.
When attackers exploit these weaknesses, organizations may face unauthorized account actions, data exposure, financial losses, and reputational damage.
Businesses should treat XSS prevention as a fundamental part of secure software development, not simply an issue to address after a security incident.
Final Thoughts
Cross-Site Scripting remains a significant web application security concern because it turns legitimate websites into potential delivery mechanisms for malicious browser code.
The most effective defenses include proper output encoding, safe DOM manipulation, HTML sanitization, strong session security, and carefully configured Content Security Policies.
Remember: Never allow untrusted input to become executable code. Treat user-controlled data as data, not instructions.